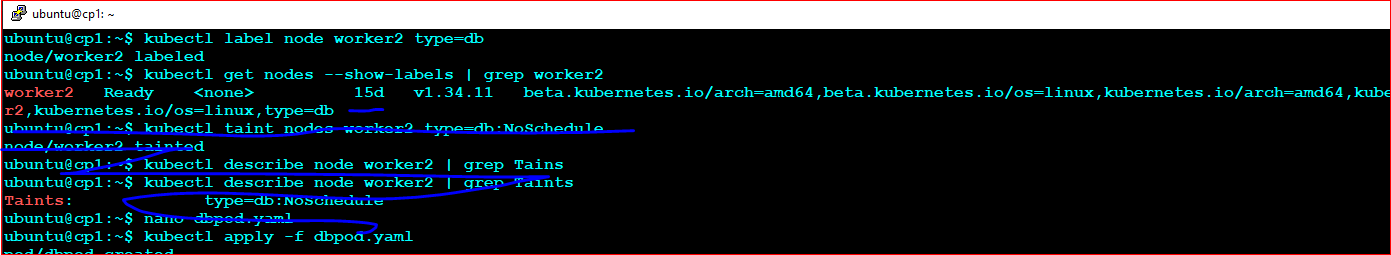
Objective: Configure node worker2 so that only workloads configured for type=db can be scheduled there. After verification, return the node to normal operation.
Add a label to identify worker2 as a database node.
kubectl label node worker2 type=db
Verify:
kubectl get nodes --show-labels | grep worker2
The taint prevents regular workloads from being scheduled on worker2. Only pods with a matching toleration will be allowed.
kubectl taint node worker2 type=db:NoSchedule
Verify:
kubectl describe node worker2 | grep Taints
Expected Output:
Taints: type=db:NoSchedule
    apiVersion: v1
    kind: Pod
    metadata:
      name: dbpod
    spec:
      nodeSelector:
        type: db
      tolerations:
      - key: "type"
        operator: "Equal"
        value: "db"
        effect: "NoSchedule"
      containers:
      - name: nginx
        image: nginx
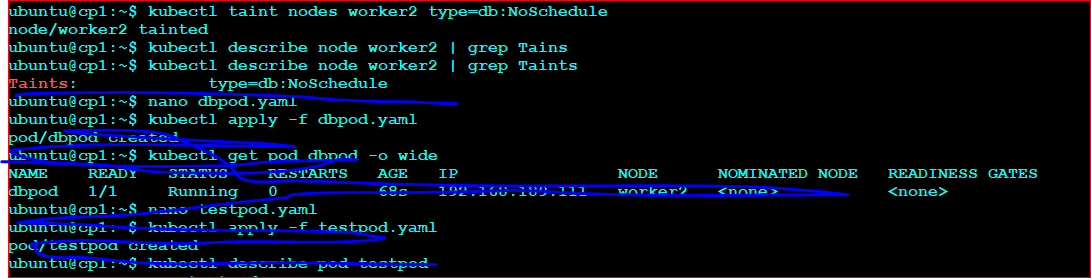
Apply:
kubectl apply -f dbpod.yaml
Verify:
kubectl get pods -o wide
Expected:
dbpod Running worker2
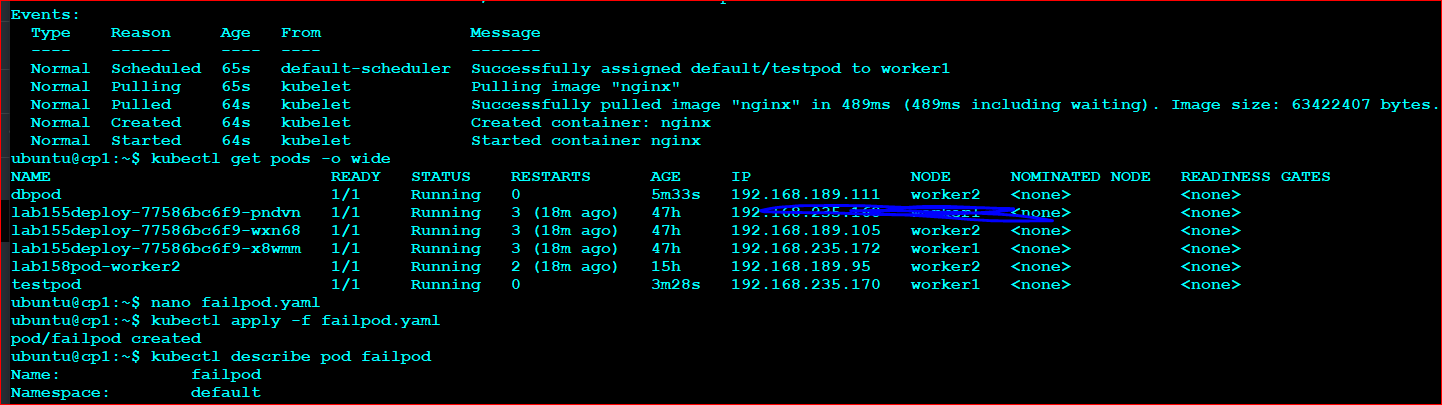
Create a regular pod without the required toleration.
kubectl run testpod --image=nginx
Check where it landed:
kubectl get pods -o wide
Example:
testpod Running worker1
This confirms Kubernetes avoided worker2 because of the taint.
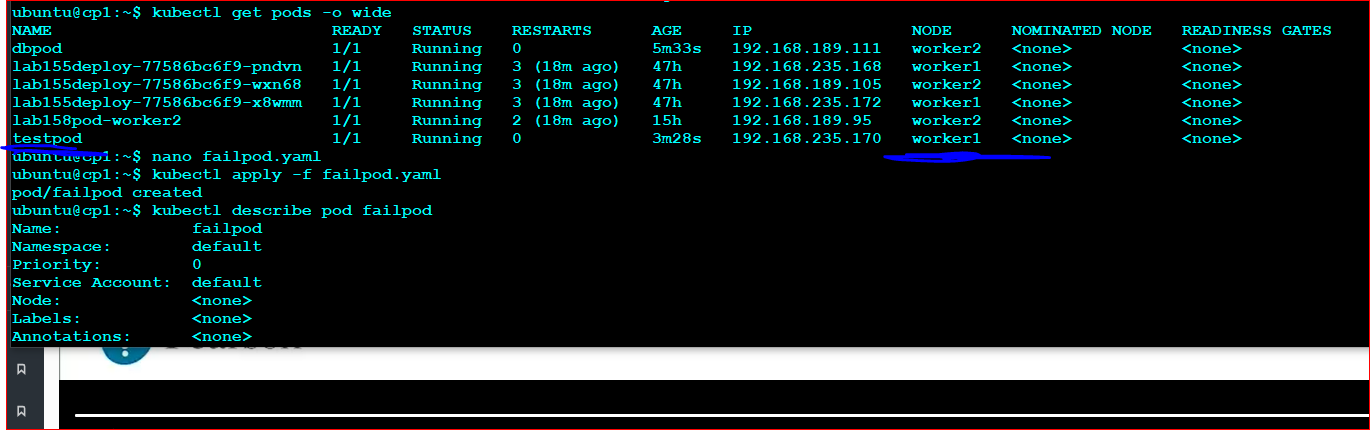
When you ran:
kubectl describe pod testpod
You saw:
Successfully assigned default/testpod to worker1
This means the restriction worked correctly. The scheduler selected worker1 because worker2 was protected by the taint.
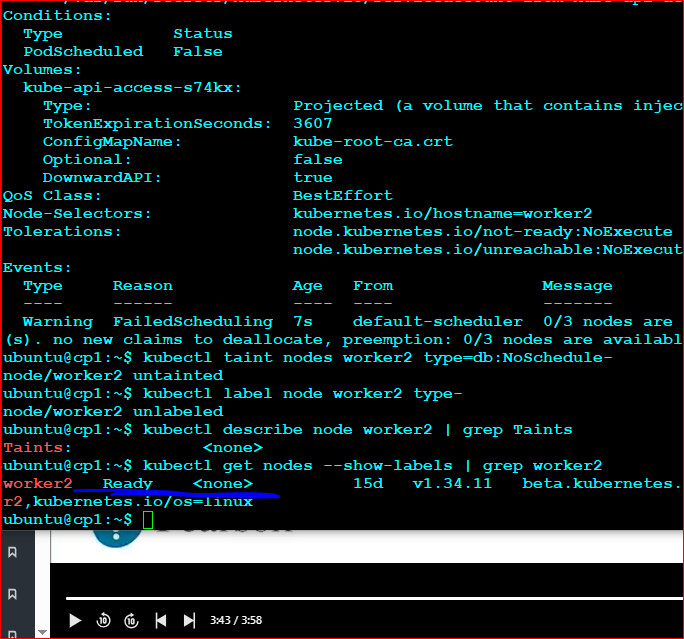
Remove the taint:
kubectl taint node worker2 type=db:NoSchedule-
Remove the label:
kubectl label node worker2 type-
Verify:
    kubectl describe node worker2 | grep Taints
    kubectl get nodes --show-labels | grep worker2
Expected:
Taints: <none>
Remember:
    Label the node
    Taint the node
    NodeSelector the pod
    Tolerate the taint
These four pieces together are one of the most common CKA scheduling tasks.